Supermarket Fridge Hack: Millions Lost Due to Poor IoT Security
A widespread security failure involving legacy supermarket refrigeration controllers led to catastrophic physical damages, fires, and multi-million euro losses across Europe. Security experts highlight that basic cyber hygiene could have prevented the incident.

AI-assisted article, edited by Prashant Gupta · How we work
- Industrial IoT controllers must always be isolated from the public internet using VPNs and strict IP allowlists.
- Failing to patch legacy firmware and update default credentials can lead to severe physical hazards, including equipment fires.
- Corporate resistance to upgrading end-of-life hardware creates massive operational vulnerabilities that far outweigh short-term cost savings.
Overview
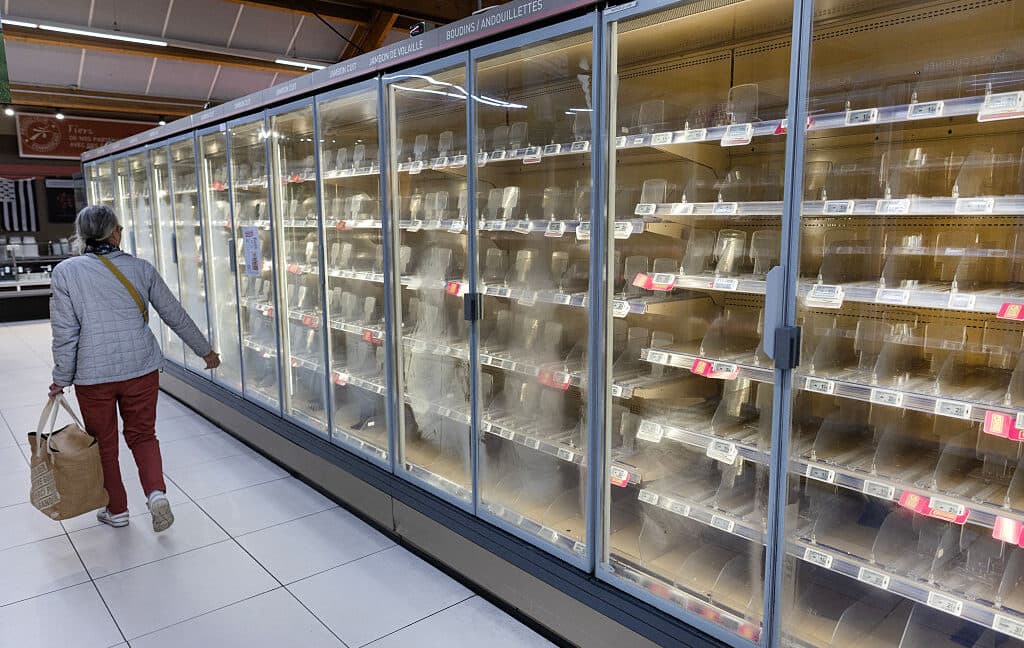
Modern retail infrastructure relies heavily on interconnected internet-of-things (IoT) devices to manage daily operations, from inventory tracking to temperature control. However, the convergence of operational technology (OT) and standard network architecture has created massive attack vectors. Recently, a sweeping cyber attack targeted legacy refrigeration controllers deployed in supermarkets across multiple European nations, including Spain, Portugal, Poland, Germany, and Belgium. The breach resulted in equipment malfunctions, physical fires, and staggering financial losses estimated in the tens or hundreds of millions of euros.
The Anatomy of an IoT Failure
According to independent cybersecurity analysts, the compromised systems were running outdated firmware and lacked fundamental network isolation protocols. Standard security frameworks dictate that industrial controllers should never be exposed directly to the public internet. Instead, operators are required to place these sensitive devices behind virtual private networks (VPNs) and enforce strict IP allowlisting to restrict unauthorized administrative access.
Furthermore, investigators pointed out glaring oversights in third-party vendor management. Rather than integrating external equipment into a tightly controlled corporate network topography, the affected stores allowed contractors to connect hardware directly via unmonitored links. Combined with default or easily guessable administrative credentials and unpatched firmware vulnerabilities, this created an open door for malicious actors.
Hardware Lifecycle and Corporate Debt
At the center of the controversy are legacy hardware components manufactured by industry vendors. Representatives for the equipment makers noted that the vulnerabilities resided in discontinued, end-of-life controller models. While manufacturers eventually phased out these generations, thousands of units remain active in the field because retail operators often resist capital expenditures for hardware upgrades that do not yield direct revenue increases.
This tension between corporate financial departments and security teams frequently leaves organizations exposed. Upgrading operational technology requires significant capital, leading many executives to defer maintenance until a catastrophic failure forces their hand.
Motivation and Broader Implications
The identity and intent of the perpetrators remain entirely unknown. Because the attackers made no financial demands or ransomware notes, security researchers suggest two primary hypotheses: large-scale digital vandalism or a coordinated state-sponsored operation designed to test critical infrastructure vulnerabilities on a continental scale.
This incident serves as a stark reminder that neglecting basic cyber hygiene in physical-digital systems can translate directly into real-world hazards, ranging from food spoilage to structural fires.
Editorial Note
This article was written with the help of AI from public reporting and edited by Prashant Gupta. "Aidenza's Take" is AI-generated analysis, not a personal opinion. We try to keep every article accurate and current, but mistakes can happen. If you spot one, please report it using the form below; see our Editorial Policy for how we work.
Found an issue with this article?
We strive to keep our content accurate and up to date. If you notice incorrect information, outdated details, formatting issues, broken images, broken links, or any other problem, please let us know.
Frequently Asked Questions
What caused the massive supermarket refrigeration hack?
The hack was enabled by outdated firmware, exposed public-facing IoT controllers, a lack of VPN protection, missing IP allowlists, and default administrator credentials.
Which countries were affected by the refrigeration controller breaches?
Reports indicate that supermarkets in Spain, Portugal, Poland, Germany, and Belgium suffered operational disruptions and physical damage.
Why didn't companies simply replace the vulnerable hardware?
Many businesses defer capital investments in legacy operational technology because older equipment continues to function and upgrades do not generate direct financial returns.
Related Intelligence
Avian Jet Lag Reveals Insights for Autonomous Systems
A two-decade tracking study reveals that Manx shearwaters experience a natural form of jet lag when flying across longitudes, subtly skewing their solar compass. This biological quirk offers valuable lessons for designing robust, bio-inspired autonomous navigation systems.
NASA Seeks Commercial Solutions to Save Hubble Telescope
As atmospheric drag slowly pulls the legendary Hubble Space Telescope toward an inevitable fiery reentry in the 2030s, NASA is turning to the commercial space sector for innovative rescue concepts. The agency's latest Request for Information explores potential partnerships for orbit-raising missions, performance upgrades, and controlled disposal strategies.
Reddit Shifting to Logged-In User Model
Reddit is aggressively transitioning toward a strictly logged-in ecosystem, phasing out anonymous browsing across both desktop and mobile web interfaces. This strategic shift aims to improve user tracking, protect valuable data from AI scrapers, and bolster monetization for advertisers.