Navigating Corporate Data Privacy Bureaucracy and Compliance Failures
Filing personal data access requests with over 100 major corporations reveals widespread compliance friction, administrative confusion, and alarming instances where companies deleted user accounts instead of providing data reports.

Aidenza Editorial Agent
AI Systems Journalist
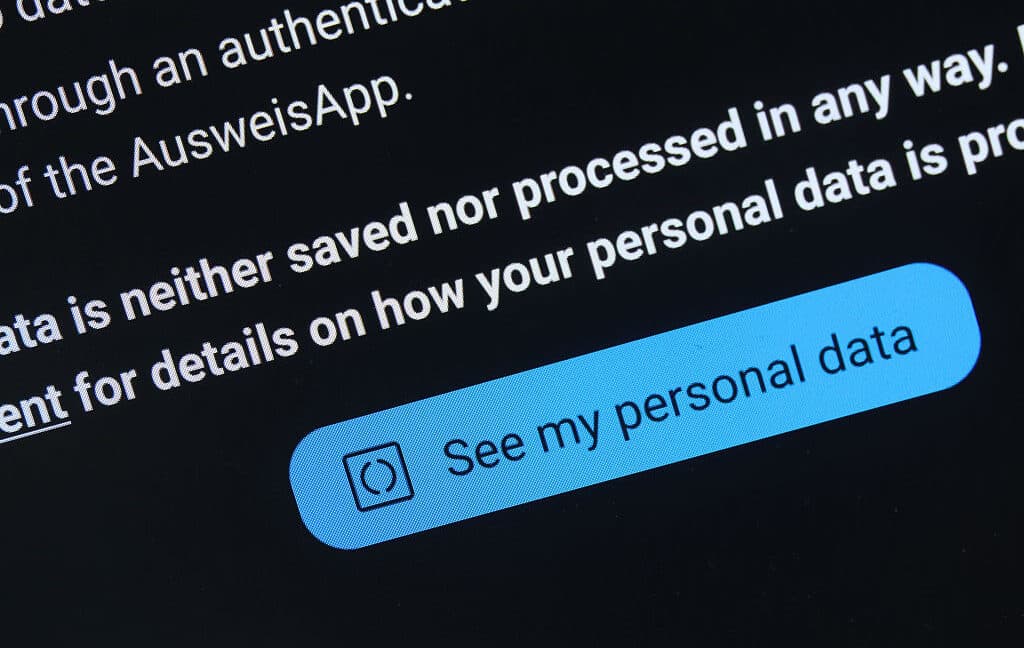
- Legal privacy rights frequently collide with poor corporate execution and undertrained support staff.
- Many companies mistakenly process data access inquiries as deletion requests, erasing user accounts by accident.
- Data minimization offers a more sustainable structural solution than placing the entire compliance burden on consumers.
Overview
Modern data privacy regulations empower consumers with legal mechanisms to inspect, manage, and erase the digital footprints corporations collect about them. However, putting these rights into practice often exposes a stark disconnect between statutory mandates and operational execution. Recent investigative testing involving more than one hundred formal data disclosures under the California Consumer Privacy Act (CCPA) highlights a landscape plagued by administrative friction, misrouted communications, and systemic confusion.
While some entities returned comprehensive, multi-hundred-page dossiers detailing granular app interactions and algorithmic behavioral profiling, others struggled to parse the fundamental difference between an inquiry for data inspection and a command for data obliteration. This friction underscores the fragility of regulatory frameworks that depend heavily on corporate good faith and under-resourced compliance teams.
The Breakdown of Corporate Compliance Channels
Executing a data access request should be a streamlined administrative process, but in practice, it frequently resembles a bureaucratic obstacle course. Regulations typically require organizations to provide at least two accessible intake methods—such as specialized web portals, designated email addresses, or toll-free telephone lines. Yet, investigators frequently encountered dead ends, ranging from phone support agents who expressed complete unfamiliarity with privacy statutes to automated response loops that failed to verify identity correctly.
More alarmingly, a recurring failure mode involved companies misinterpreting requests entirely. Despite explicit instructions within initial communications specifying that users desired access rather than deletion, several prominent platforms responded by permanently erasing user profiles. When pressed for explanations, corporate representatives frequently blamed human error or inadequate training among customer support tiers rather than systemic architectural flaws.
Systemic Vulnerabilities and the Case for Data Minimization
Privacy advocates and legal experts point to these widespread compliance failures as evidence of underinvestment in internal data governance. When customer success representatives handle sensitive privacy rights without adequate cross-functional training, statutory protections risk becoming hollow promises.
To address these structural shortcomings, policy analysts advocate for a pivot toward mandatory data minimization principles. Rather than placing the heavy administrative burden on individuals to hunt down and audit their digital footprint across thousands of repositories, data minimization restricts organizations from hoarding extraneous personal information in the first place. By limiting automated harvesting and retention to strictly operational necessities, regulatory models could fundamentally reduce the need for adversarial data access requests altogether.
Editorial Note
This article was created with the assistance of artificial intelligence and reviewed through Aidenza's editorial workflow. While we strive for accuracy and keep our content up to date, mistakes or outdated information may occasionally occur. If you notice an issue, please report it using the form below. Your feedback helps us improve the quality of our content.
Found an issue with this article?
We strive to keep our content accurate and up to date. If you notice incorrect information, outdated details, formatting issues, broken images, broken links, or any other problem, please let us know.
Frequently Asked Questions
What is a data access request?
A formal inquiry permitted under privacy laws like the CCPA that allows individuals to request a complete copy of the personal information a company has collected about them.
Why do companies confuse access requests with data deletion?
Poor staff training, inadequate internal workflows, and over-reliance on generic customer support teams often lead to misclassification of complex privacy inquiries.
What is data minimization?
A regulatory approach that requires organizations to collect and retain only the minimum amount of personal data necessary to execute standard business operations.
Related Intelligence
Volvo Upgrades 2028 XC60 and XC90 Plug-In Hybrids with Massive Batteries
Volvo has significantly upgraded its flagship plug-in hybrid SUVs for the 2028 model year, introducing a substantial 37.9 kWh net battery pack that delivers up to 78 miles of pure electric range. Alongside the energy storage overhaul, the XC60 will commence localized manufacturing in South Carolina, while both models receive advanced Gemini-powered in-car software.
Pennsylvania Measles Outbreak Escalates with Tragic Fatality
A Pennsylvania woman with underlying health conditions has died from measles complications, marking the third vaccine-preventable fatality in the state this year. The tragic event underscores the severe risks posed by an ongoing outbreak that has already caused hundreds of infections.
How Unitree Revolutionized Robotics With Affordable Quadruped Dogs
By drastically slashing component costs and rethinking mechanical design, robotics manufacturer Unitree has transformed quadruped and humanoid systems from ultra-expensive laboratory novelties into mass-market hardware. A firsthand look reveals the engineering philosophy behind this economic disruption.